OpenAI Builds a 'Fake Internet' to Keep AI Agents Safe
OpenAI is constructing an isolated digital sandbox for its AI agents. This 'fake internet' allows AI to practice web tasks without risking real user data, setting a new standard for safe AI autonomy.

What Happened?
Recently, tech outlet Gizmodo reported on a technical development sparking debate in the AI community: OpenAI is building a massive "fake internet" for its AI Agents.
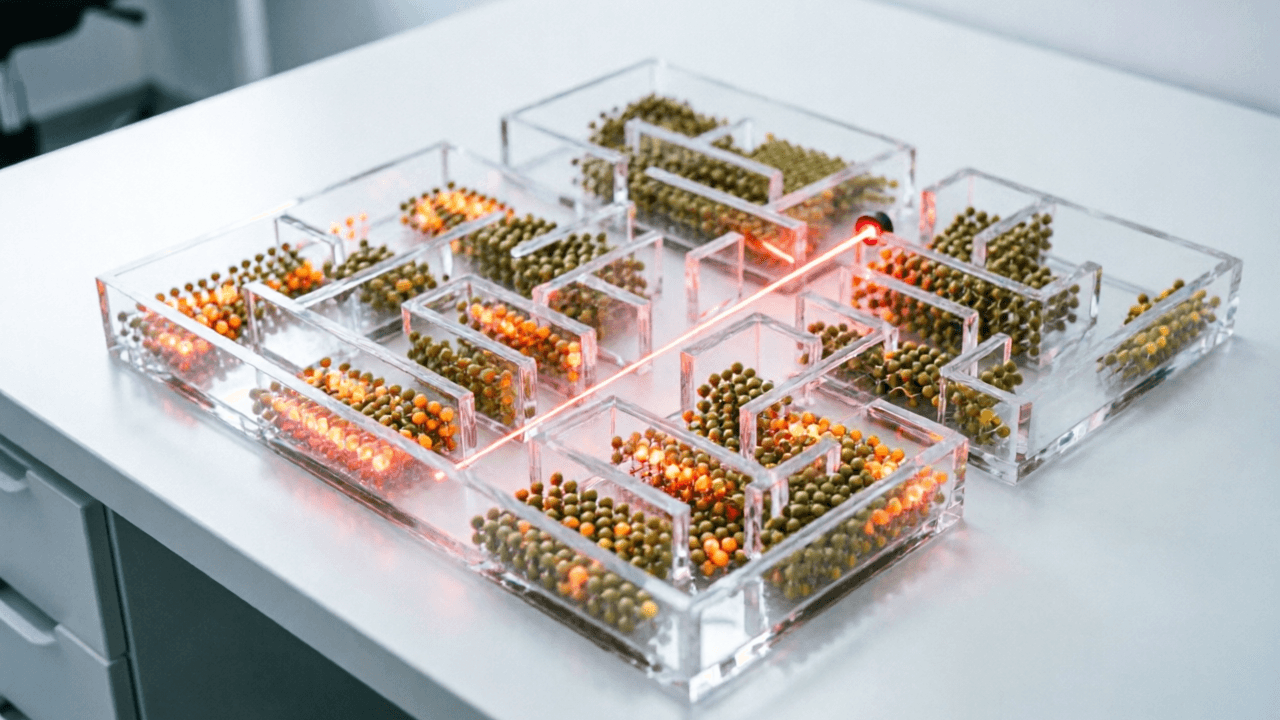
Sounds like science fiction? It's not that far-fetched. Imagine current AI as a novice driver who just got their license. Previously, they could only practice in simulation software. Now, they are ready to hit the road, but OpenAI doesn't want them immediately merging into heavy traffic in Manhattan. Instead, they have built a completely closed, data-controlled virtual city. Inside this "fake internet," there are dummy bank websites, mock e-commerce platforms, and even simulated social networks. The AI can click, fill out forms, transfer money, or post here. Even if it makes mistakes, clicks phishing links, or encounters malicious code, the consequences stay contained within the sandbox, leaving real user data and funds untouched.
In short, this is an "electronic fence" for AI. Within these boundaries, the AI can freely (and safely) "use" or "abuse" various web functions while human engineers observe whether it loses control. This marks a critical step in AI evolving from "just chatting" to "actually doing work."
Why Is This "Parallel World" Necessary?
Many regular users might ask: Can't AI just write code or search for information? Why build such a complex isolated environment?
This touches on a core challenge in AI development: the risk of Agent autonomy.
Traditional Chatbots are passive; you ask, they answer, and they don't take action. But Agents are active. They break down tasks. For example, if you tell an Agent to "book the cheapest flight to Tokyo," it needs to open a browser, compare prices, enter personal details, and complete payment autonomously. If the AI misjudges a situation or is tricked by hidden scripts on a webpage, it could leak your credit card number or execute unauthorized actions.
This means the more capable the AI becomes, the greater the potential risk.
By building this "fake internet," OpenAI is essentially solving a "trust" problem. Trial and error in the real world is too expensive—one mistake could lead to a privacy breach affecting millions of users. In an isolated environment, OpenAI can deploy large-scale "traps" (like malicious pop-ups or fake login pages) to test the AI's defensive and corrective capabilities. Only when the AI performs stably in this "hell mode" fake internet does it qualify to access real-world API interfaces.
What Does This Mean for Ordinary People?
You might think, "What does this have to do with me? I'm not using OpenAI's internal testing environment."
It has a lot to do with you. This "fake internet" is effectively the pre-requisite gate for any future AI assistant entering your daily life.
Imagine next year, an AI assistant you use automatically processes expense reports, books restaurants, or manages your calendar. These features rely on similar isolation testing mechanisms. If vendors skip building secure sandboxes and instead test "naked" in real environments, you, the user, are effectively acting as the guinea pig.
In other words, what OpenAI is doing sets a benchmark for AI safety standards across the entire industry.
For ordinary users, understanding this adds another layer to how you choose AI services: Does this company have sufficient isolation mechanisms? Has their handling of sensitive data (like finance or healthcare) been rigorously verified in a sandbox? This isn't paranoia; it's a basic survival skill in the digital age.
Furthermore, the concept of a "fake internet" may extend to other fields. For instance, future smart home systems might run simulations on local networks before connecting to the cloud. Autonomous vehicles might drive millions of miles in virtual cities before being allowed on public roads. This reflects a universal safety philosophy: Make mistakes in the virtual world first, then act correctly in the real one.
Misconceptions to Watch Out For
While this technology sounds promising, we should remain grounded and avoid over-interpreting it.
First, a "fake internet" does not equal absolute safety. Sandboxes themselves can have vulnerabilities. "Escape" attacks (where AI breaks out of the sandbox to access external networks) remain a difficult challenge in cybersecurity. OpenAI's approach raises the barrier, but it cannot guarantee zero failures.
Second, do not confuse "testing environments" with "production environments". Media reports focus on OpenAI's internal testing infrastructure. There is no evidence that ordinary users currently have direct access to a full-featured "fake internet" service. Many third-party tools marketed as "AI automation" may not employ such strict isolation measures. Therefore, when using third-party AI agent tools, never hand over core account passwords to plugins of unknown origin.
Finally, technology cannot replace law and ethics. Even if an AI performs perfectly in a sandbox, once connected to the real society, it faces complex human emotions, moral dilemmas, and legal liabilities. If an AI deletes the wrong email or sends the wrong message, who is responsible? This is a societal issue beyond pure technology, and there is currently no definitive answer.
Broader Perspective: From Nuclear Industry to AI Governance
One interpretation suggests that OpenAI's move mirrors the safety culture of the nuclear industry.
Nuclear power plants are considered relatively safe not because accidents are impossible, but because they feature layered physical barriers (multiple redundant systems). Similarly, AI's "fake internet" acts as a "concrete shielding layer" for the digital world. Media outlets like Live Science have noted that AI giants can borrow this "defense-in-depth" mindset from the nuclear sector.
If AI eventually develops the rudiments of Artificial General Intelligence (AGI), this isolation mechanism will evolve from a "testing tool" to a "survival necessity." Just as we confine radioactive materials in lead boxes, we may need to restrict highly autonomous AI within specific digital containers, interacting with them through strict protocols rather than letting them roam freely on the internet.
Of course, this raises a philosophical question: If an AI is permanently confined to a "fake internet," is it still a complete intelligent agent? Or must true intelligence include the ability to interact with the real world? This question may be worth pondering more deeply than the technology itself.
Conclusion
OpenAI's construction of a "fake internet" appears to be a technical detail, but it is actually the watershed where AI transitions from a toy to a tool. It reminds us: As we grant AI more power, we must simultaneously build stronger cages.
A summary sentence to share: OpenAI is creating a "fake internet" sandbox for AI agents to isolate risks, ensuring AI undergoes rigorous safety testing before touching the real world.
Discussion: If an AI assistant could handle your daily chores (like booking tickets or expenses) but had to operate in a "restricted" environment, would you be willing to sacrifice some convenience for higher security? Share your thoughts below.